

Jun 01, 2026, 12:35 PM
(This post was last modified: Jun 01, 2026, 12:46 PM by solitaryElite.)
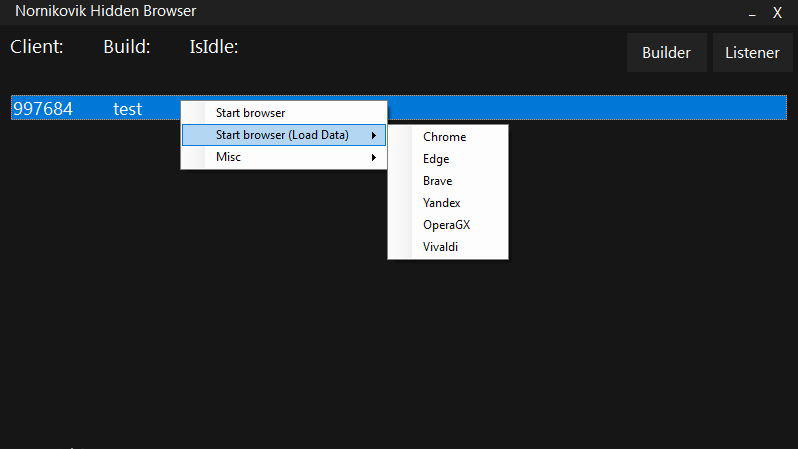
You can load browser data (cookies & autofills), the browser runs on the background of their pc, you can control it smoothly from your side, a new desktop is not created. The malware is fileless, sometime after it's executed it will delete itself, and then persistently runs without it being on disk, note that it will drop some artifacts on disk from cefsharp, as well as copy the user's browser data, but these are legit files, not malware.
Supported browsers: Chrome, Edge, Brave, Yandex, OperaGX, Vivaldi.
Undetected, for how long? I don't know, pay me more money if you want a private stub (politely)
You can also just run from memory/crypt it easily.
5 Persistence methods
AntiVM/Analysis & related
Binder
Size pumper
Msgbox
Output: .exe / .bat / .lnk(no smartscreen warning) / .cpl (no smartscreen warning if ran from inside archive) / .dll(.net) / .dll (native)
Autobuy: https://nornikovik.sell.app/product/nornikovik
If you have any questions, or want to use mm, you can contact me.
tox: BD25FB41D99E9CB59F6F02941E5734EB5B1F21F16687A5A6A2192FC445023537636E55B6C6F7
We can use the forum's official mm service: http://breachqr3dqbysbq5khaadg5ynnpxn2wr...an-Service