May 27, 2026, 08:45 AM
(This post was last modified: May 27, 2026, 09:33 AM by noonetrust.)
The issue originates from a publicly accessible application endpoint that unintentionally returns downloadable SQL backup database files (.sql).
Affected Platform:
- SITOMAS Application
- Managed by: Magelang City Government
- Country: Indonesia
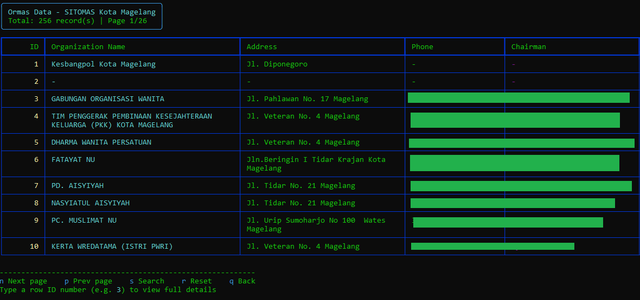
The exposed SQL backup appears to contain approximately 250 tables related to community organization (Organisasi Masyarakat / ORMAS) administration and internal platform management.
Observed data structures include:
- Chairman full names
- Treasurer full names
- Full addresses
- Phone numbers
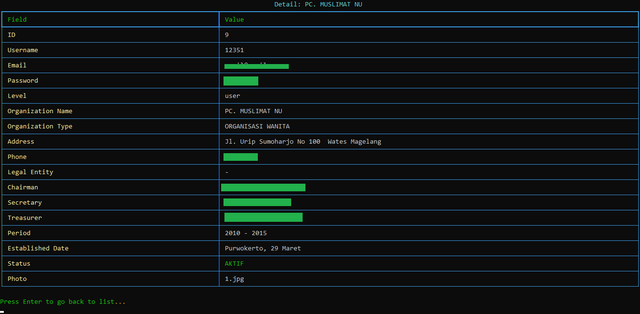
- Email addresses
- Usernames
- Password fields
- Customer names & emails
- Internal user tables containing usernames, passwords, and emails
Important Disclaimer:
- No sensitive or personal data will be publicly shared in this thread.
- This post is intended solely to document and validate the existence of the exposure.
To verify the legitimacy of the issue, a validation package containing a Proof-of-Concept (PoC) tool is available.
- Download: https://gofile.io/d/mQlpsC
- ZIP Password: G6lukYbnE#iaCN33
Status:
- Exposure confirmed
- Public endpoint accessible at time of writing
- Responsible disclosure status unknown