Sep 06, 2024, 02:29 AM
Let's discuss the pwn challenge

|
HTB - Scanner (Challenge)
by x1rx - Friday September 6, 2024 at 02:29 AM
|
|
Sep 06, 2024, 02:29 AM
Let's discuss the pwn challenge
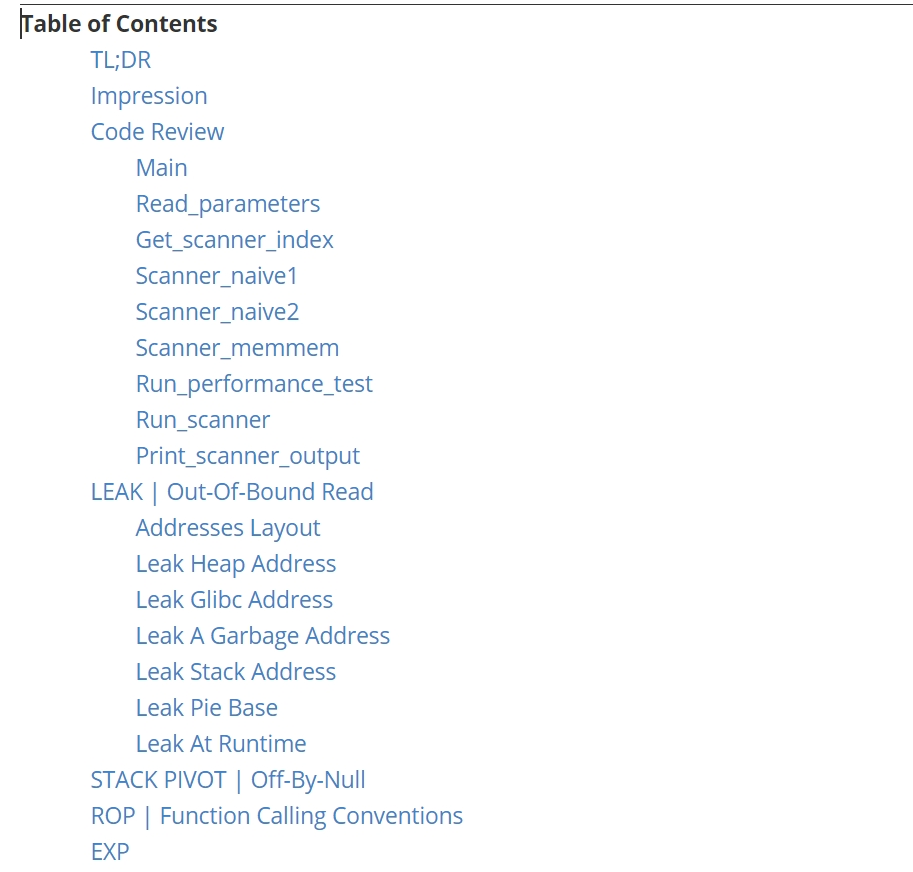 http://4xura.com/wp-content/uploads/2024...bf_all.jpg These hints should be enough to show you the path finishing the exploit part. Enjoy
Sep 07, 2024, 06:19 AM
(Sep 07, 2024, 03:28 AM)Axura Wrote: My instance always gets fcked up! lol 
1 - heap leak
2 - libc leak 3 - rbp leak 4 - stack pivot --> new rbp with off by null 5 - rop chain 6 - hijack execution flow All steps are done and I got the flag(while loop) but my script is unstable . When I use off by null and pivoting on stack , process crashes . What am I missing? any hint
Mar 12, 2025, 06:06 AM
this is a good initiative will like to see this
will appreciate if got it free |
|
« Next Oldest | Next Newest »
|
| Possibly Related Threads… | |||||
| Thread | Author | Replies | Views | Last Post | |

|
[FREE] HackTheBox All Cheatsheets | 84 | 11,164 |
8 hours ago Last Post: groningen1981 |
|
| [MEGALEAK] HackTheBox ProLabs, Fortress, Endgame - Alchemy, 250 Flags, leak htb-bot | 165 | 34,661 |
8 hours ago Last Post: groningen1981 |
||
| Finding solutions/flags/writeups for challenges | 0 | 129 |
Today, 04:13 AM Last Post: meomeothantai |
||
| [FREE] HackTheBox Dante - complete writeup written by Tamarisk | 625 | 115,333 |
Today, 03:26 AM Last Post: kevin25hxl |
||
| [FREE] CPTS 12 FLAGS | 168 | 19,540 |
Today, 12:57 AM Last Post: blooper1337 |
||